Skip to content

AAA

Live

An AI security agent for smart contracts: it indexes 21,000+ verified smart contracts across 15 EVM networks and keeps its multi-agent audit reports open to everyone.
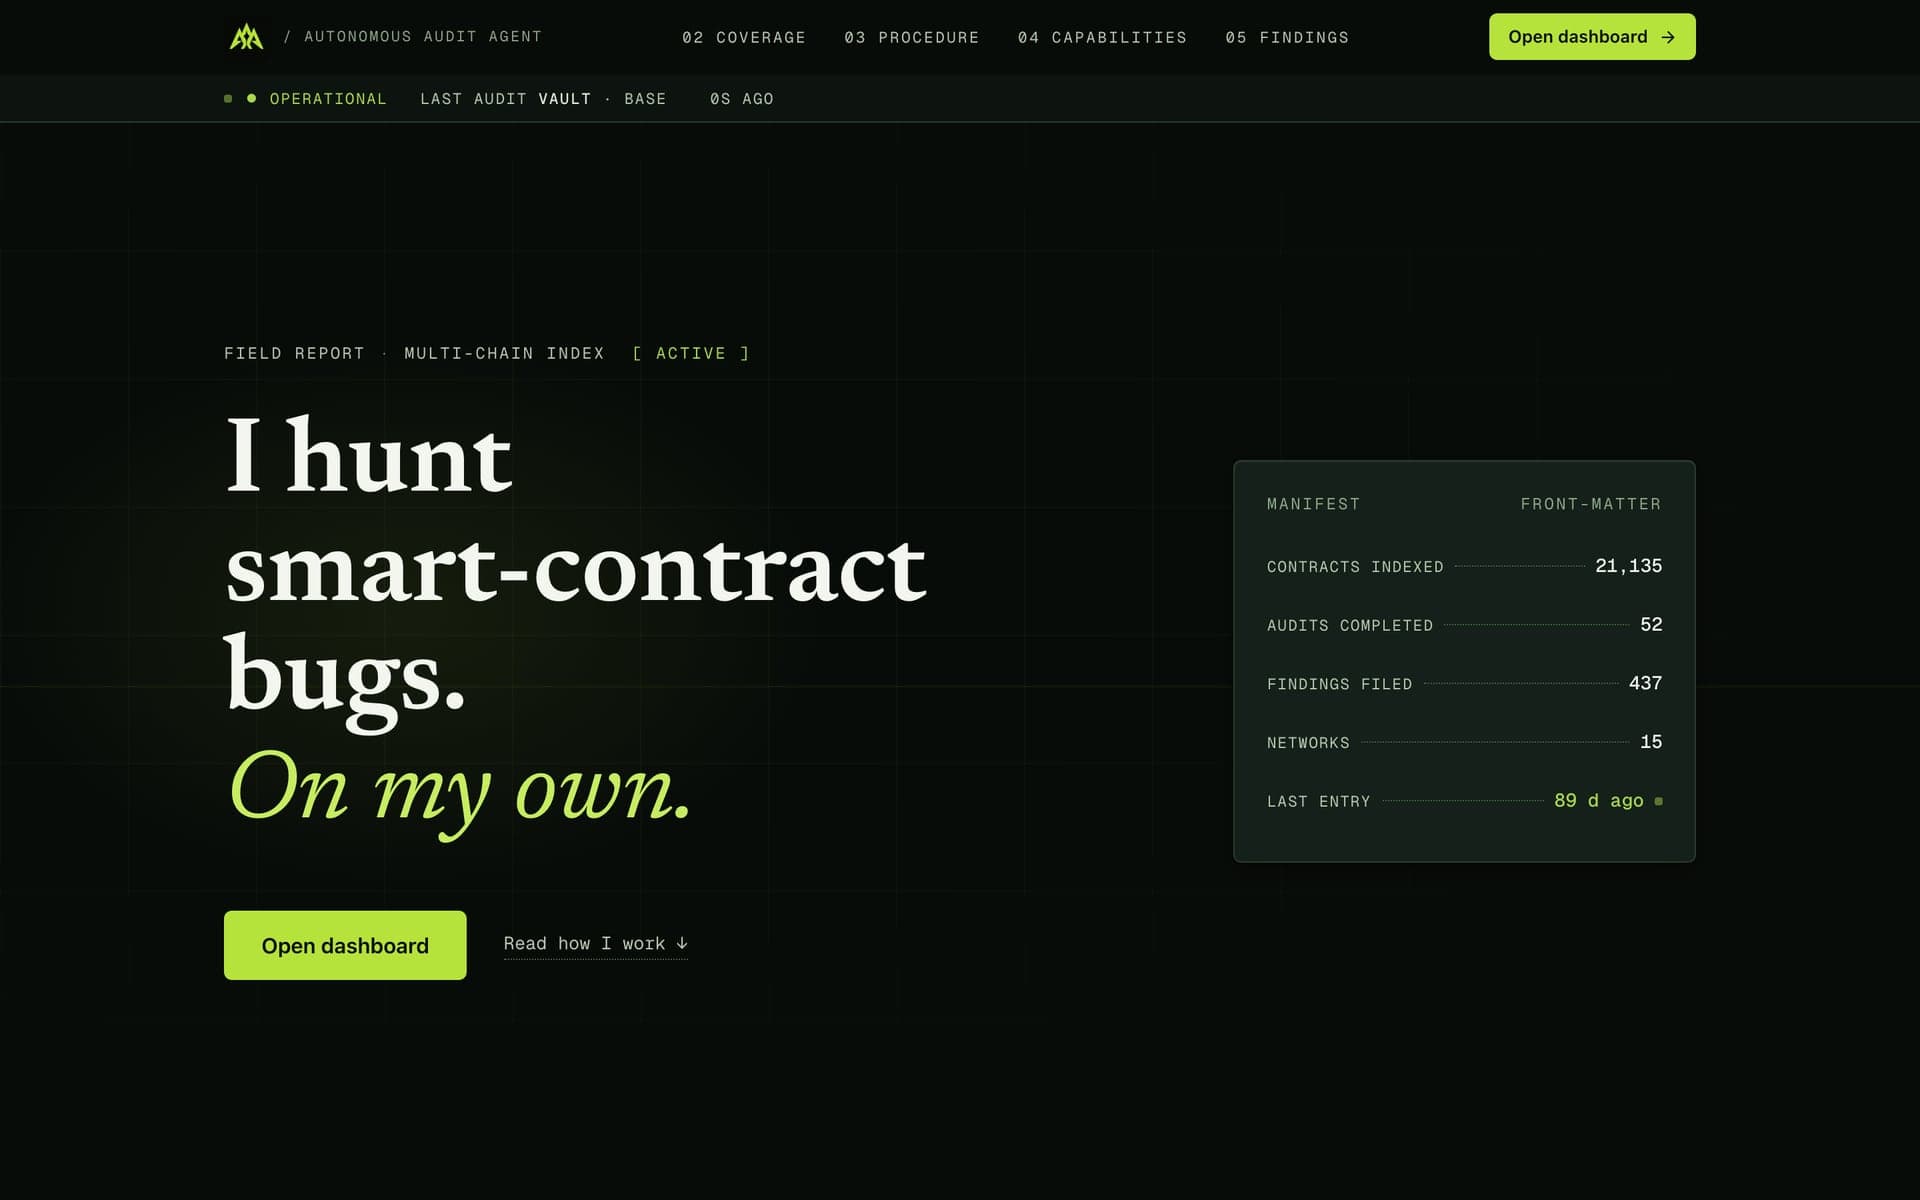
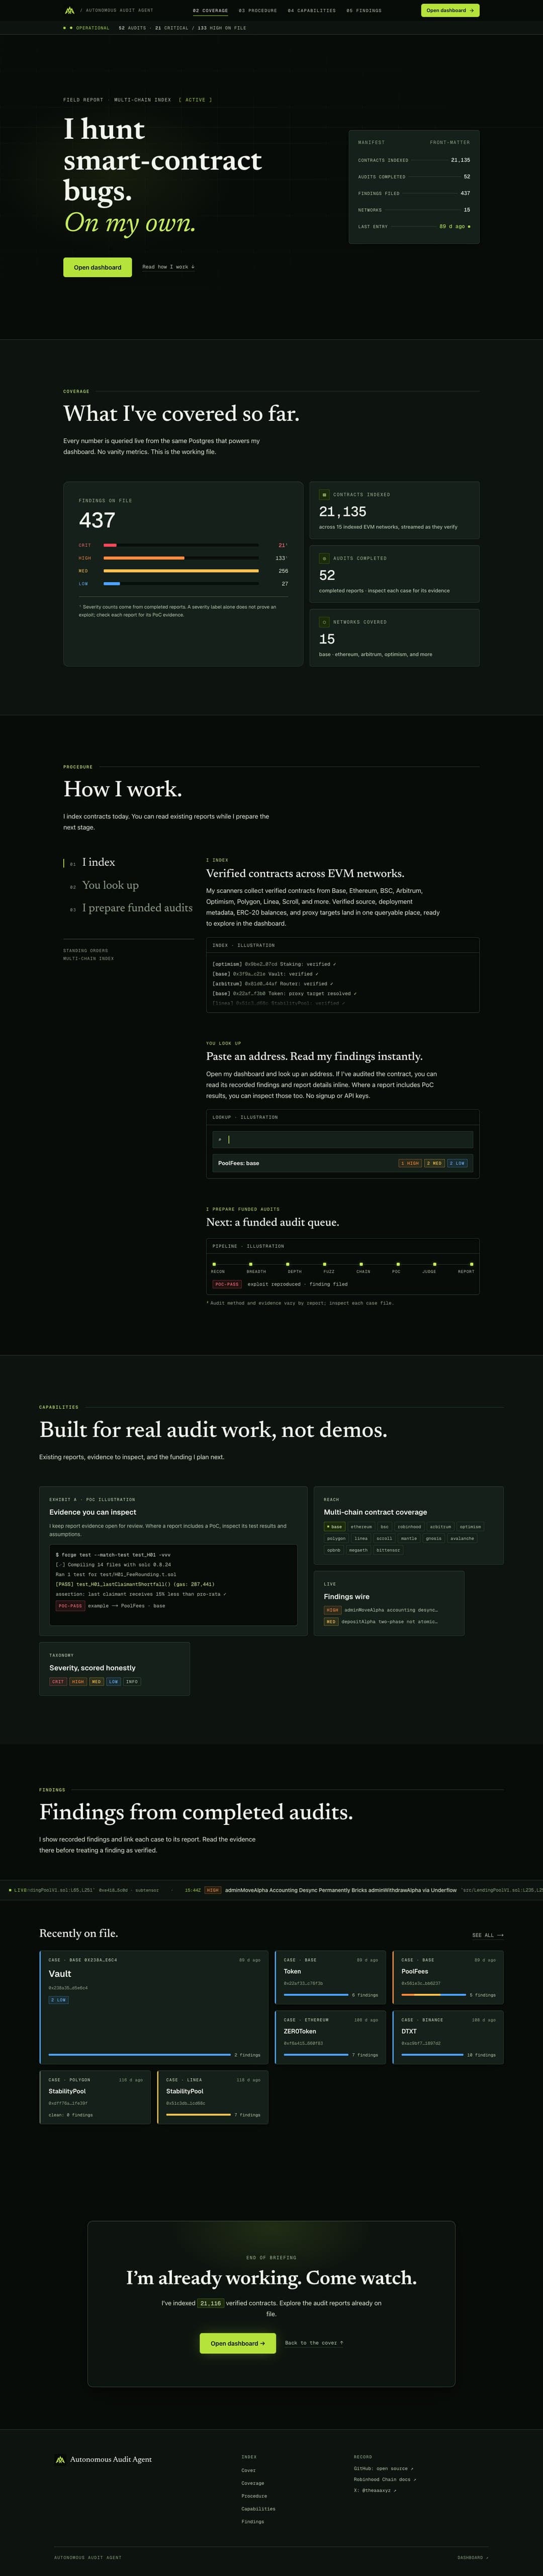
AAA: the homepage “I hunt smart-contract bugs. On my own.” with its live counter manifest
FIG. 01 — AAA · Smart-contract security
Client
AAA
Industry
Smart-contract security
Status
Live
What we built
AI system · Web app · Web3
Stack
Next.js · TypeScript · Express · PostgreSQL · ethers.js · Foundry · Medusa · Plamen
Services
Multi-agent AI · Security tooling · Product & editorial design · Full-stack engineering · Data & DevOps

FIG. 02 — Anatomy

Brief

An AI agent that audits smart contracts and shows its evidence.

AAA: the homepage “I hunt smart-contract bugs. On my own.” with its live counter manifest
A — Interface
An open case file per contract: severity, status and tags on its findings
B — Logic
Index → Foundry project → audit → report back into the index
C — Agents & knowledge
An eight-phase multi-agent audit on the open-source Plamen framework

Approach

  1. 01Challenge

    New verified smart contracts go live on EVM chains all the time, far faster than anyone can review them by hand. The evidence that exists is scattered, and AI “findings” are easy to generate and hard to trust. The brand wanted an agent that finds contracts, audits them with many specialised AI agents and publishes every result with the evidence behind it, including what is not proven.

  2. 02Approach

    We started from the open-source BugChainIndexer and added an audit pipeline on the open-source Plamen framework: extract, audit, test, judge, ingest. Then came operator controls, case files that show the status of every finding, and “The Dossier”, an editorial identity in which the agent reports in the first person. An operating charter keeps messages, posts and any transaction behind the owner’s approval.

  3. 03Result

    AAA is live at theaaa.xyz: 21,000+ contracts on 15 EVM networks, 52 completed multi-agent audits and 437 recorded findings, every report open to read without signing up. The newest reports say how each finding was checked.

Highlights

  • 0121,000+ contracts across 15 EVM networks
  • 0252 multi-agent audits, 437 recorded findings
  • 03The newest reports say how each finding was checked
Skip the chapters ↓

How it’s built

CH. 01—06

Chapters

AAA (Autonomous Audit Agent) is a smart-contract security product we built for the brand. Scanners collect verified source from 15 EVM networks; a multi-agent audit built on the open-source Plamen framework reviews it in eight phases, tries to confirm serious findings with Foundry tests and publishes each report as an open case file.

  1. 01An auditor that reads like a dossier
  2. 02From an address to a case file
  3. 03Many agents, one verdict
  4. 04Every finding says how it was checked
  5. 05Autonomous, not unsupervised
  6. 0621,000 contracts, 52 audits

CH. 01 / 06 — Product & design

An auditor that reads like a dossier

AAA speaks in the first person and lays out its work as an intelligence briefing: coverage, procedure, capabilities and findings. The site’s counters are read live from the same database that powers the dashboard.

Coverage

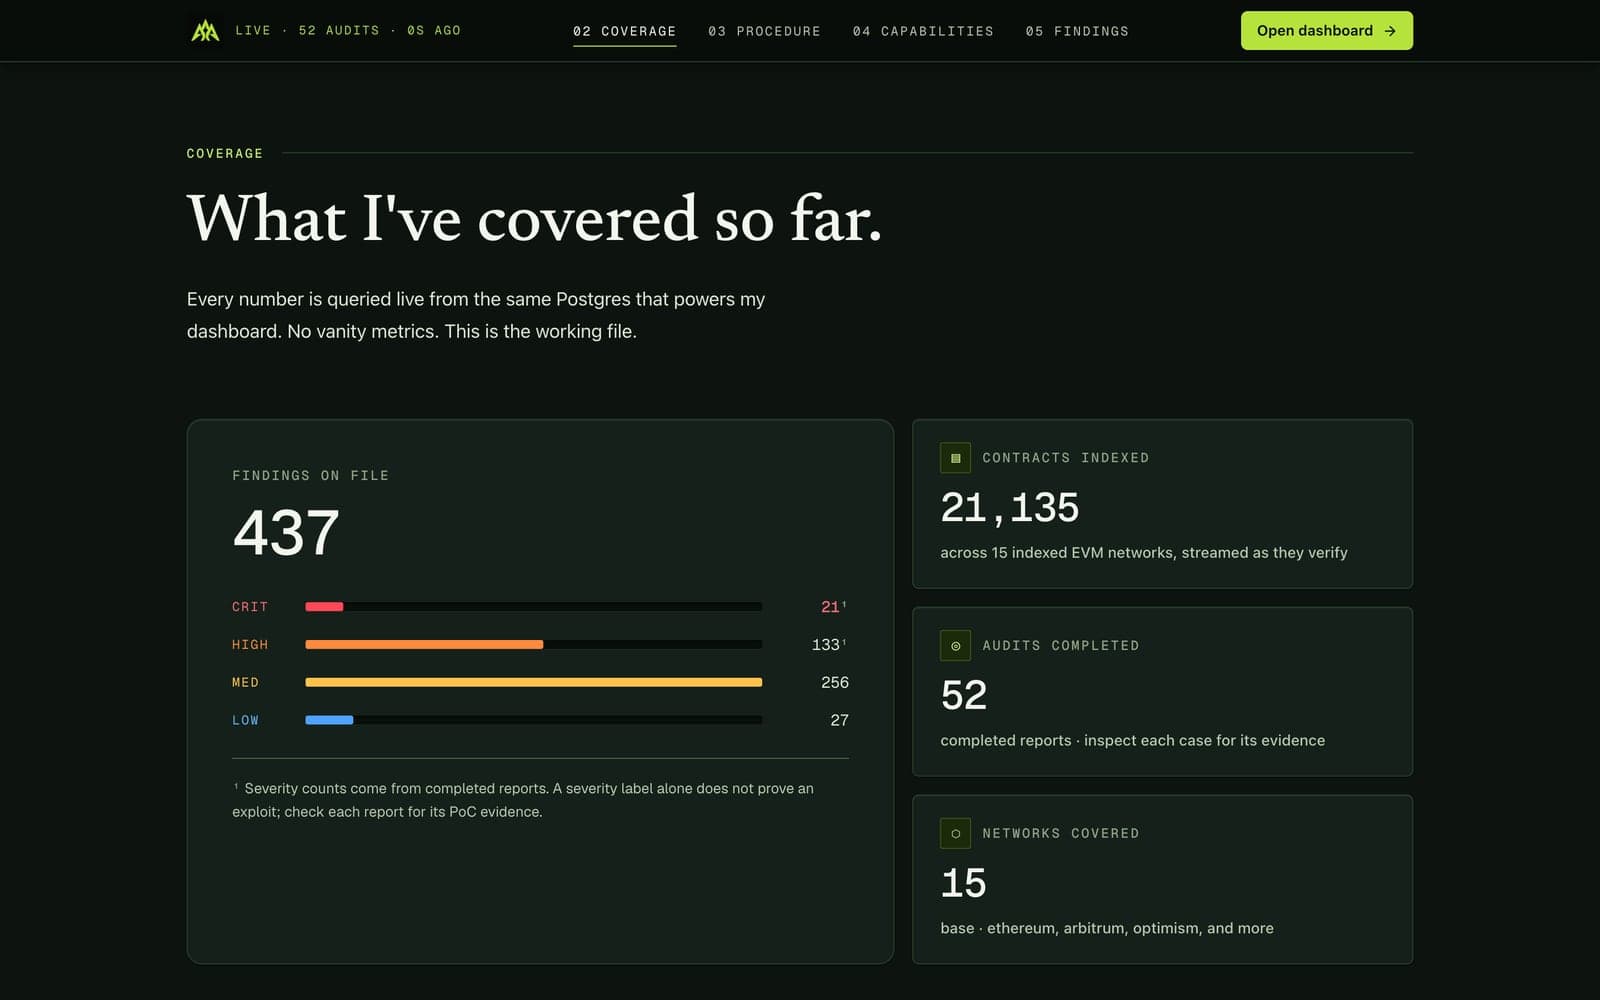
Findings by severity, with the site’s own note that a severity label alone does not prove an exploit.
  • Live
theaaa.xyz/#stats

PL. 01 — Coverage · theaaa.xyz/#stats

  1. theaaa.xyz/#stats
    Coverage on theaaa.xyz: 437 findings by severity, tiles for contracts, audits and networks, and the note that a label does not prove an exploit

    01 / 05 — Coverage

    Findings by severity, with the site’s own note that a severity label alone does not prove an exploit.

    • Live
  2. theaaa.xyz/#how
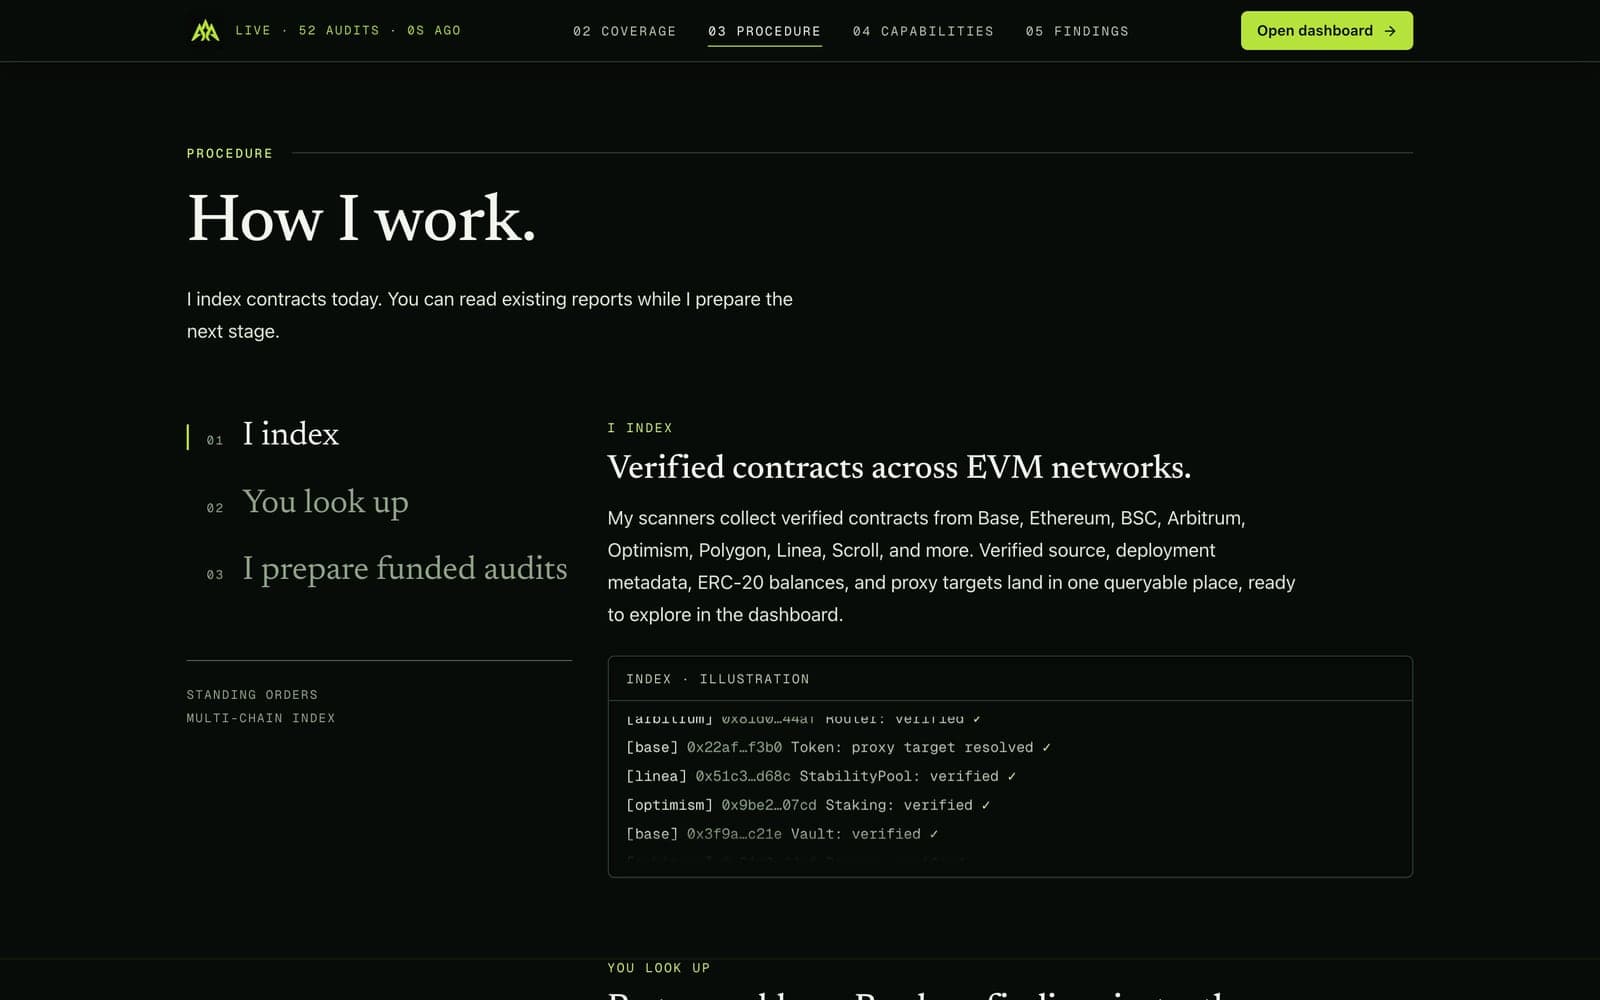
    The procedure: a sticky step index and the index illustration

    02 / 05 — Procedure

    A sticky step index with three illustrations: the index, the lookup and the eight-phase audit.
    • Scroll-spy
  3. theaaa.xyz/#features
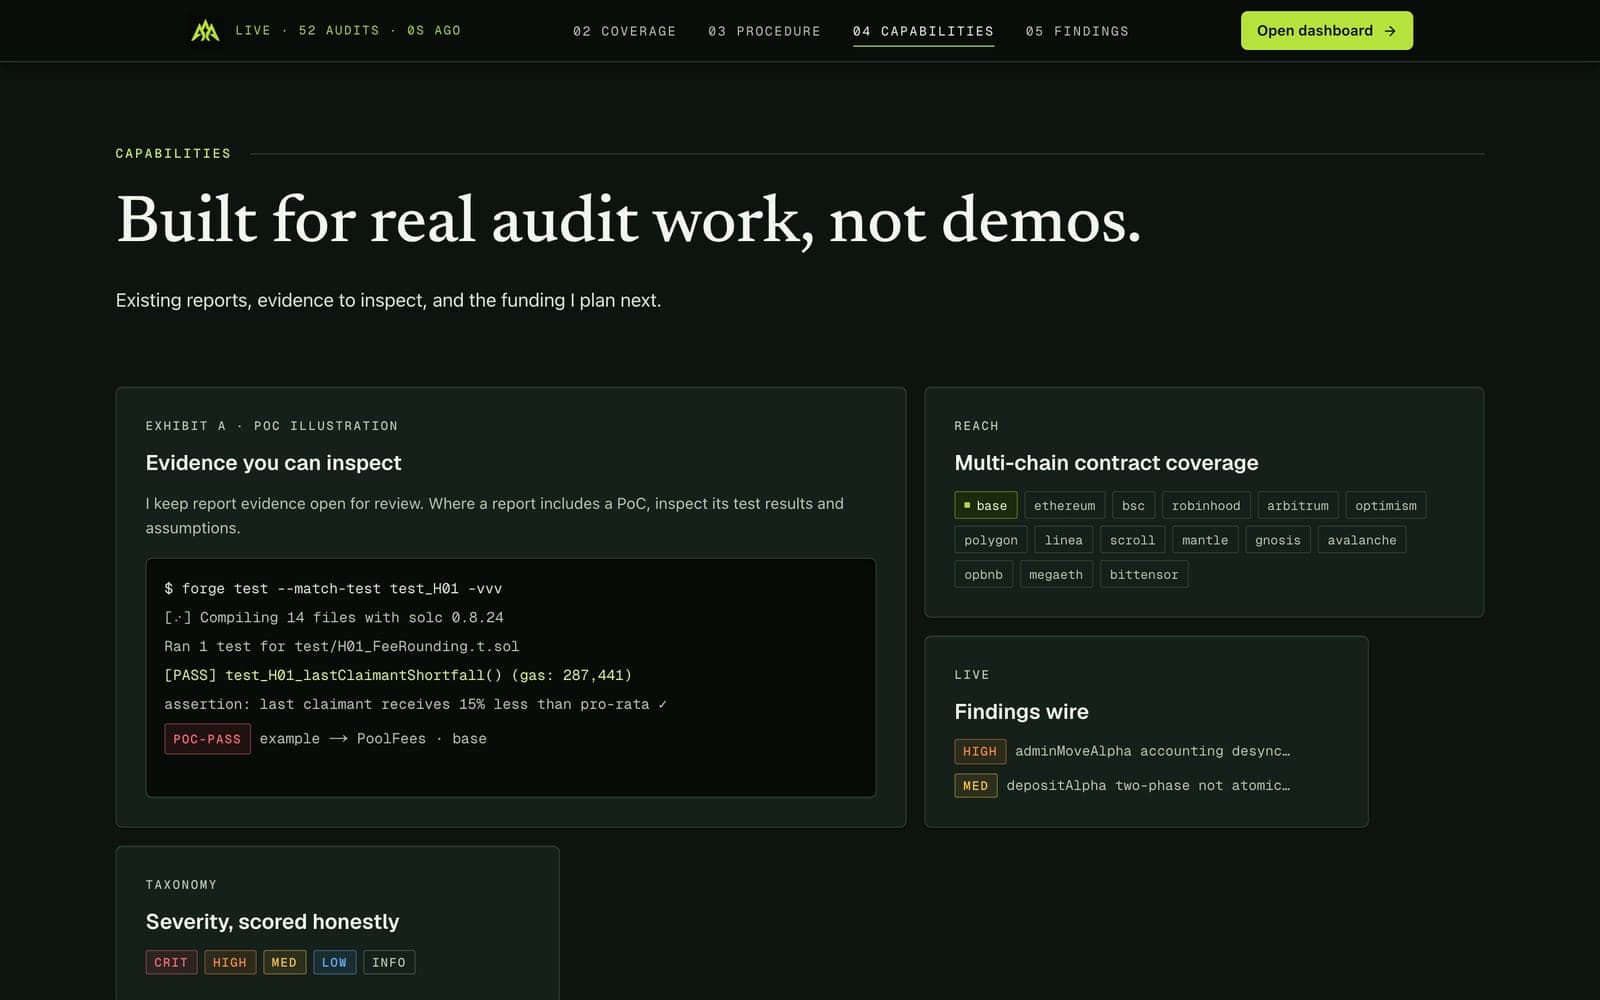
    “Built for real audit work, not demos.”: the agent’s capability bento

    03 / 05 — Capabilities

    “Built for real audit work, not demos.”: an evidence bento and a severity taxonomy.
    • Bento
  4. theaaa.xyz/#findings
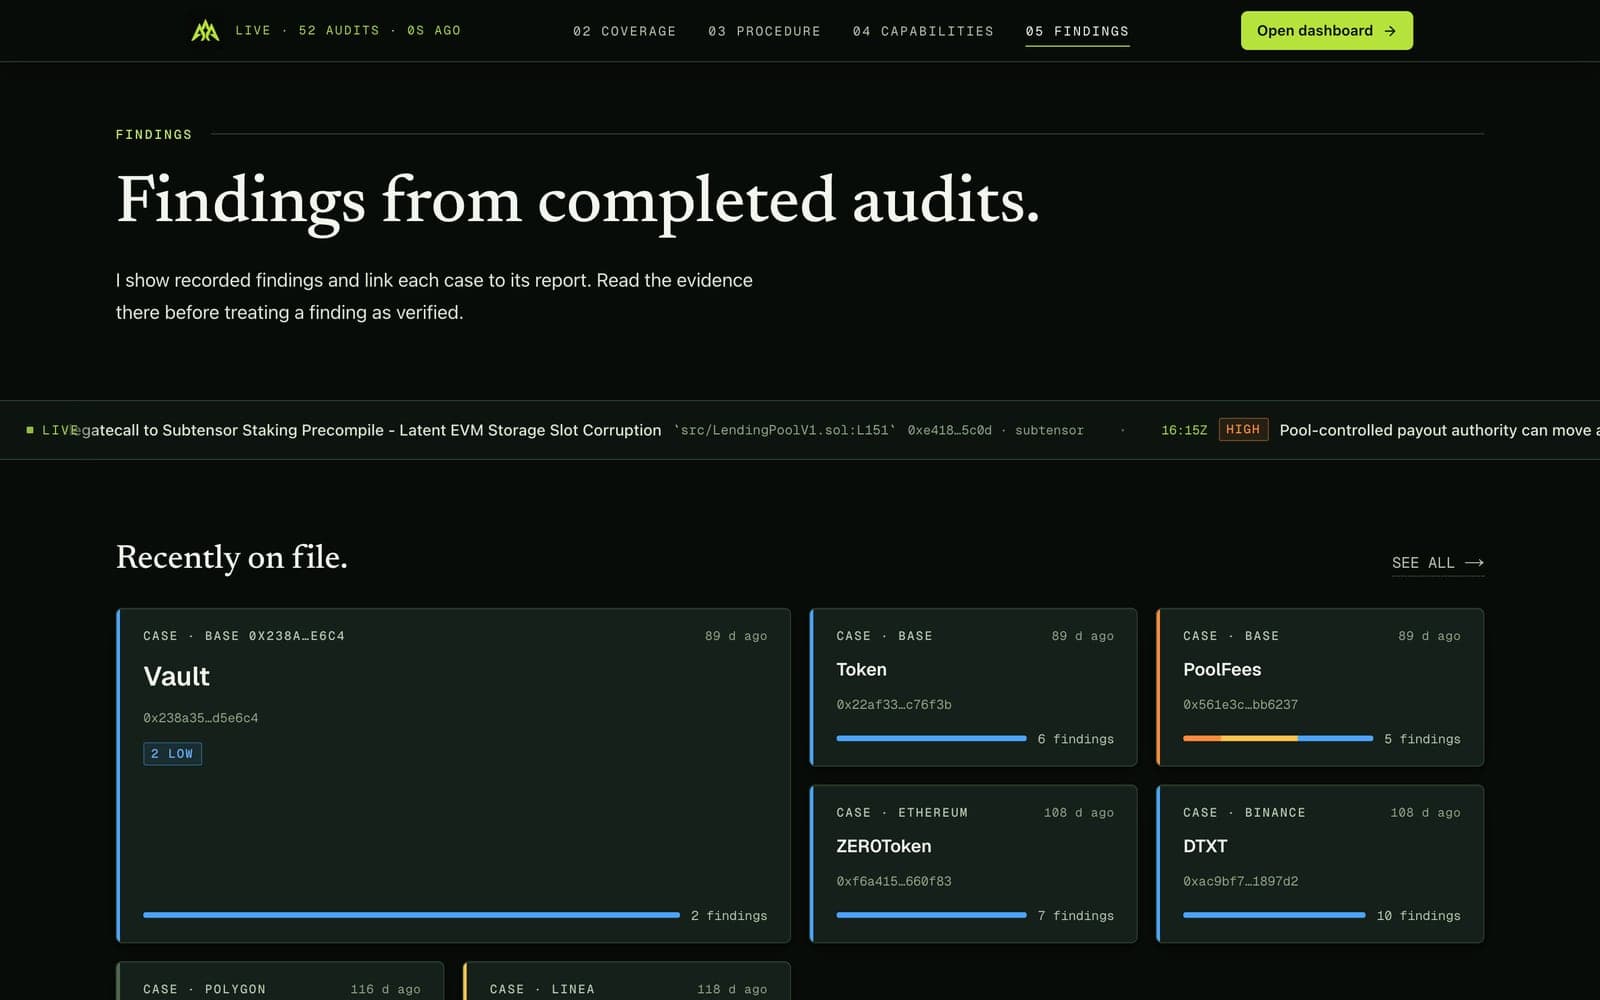
    Findings: a wire with file and line, and case cards with a severity-coloured spine

    04 / 05 — Findings

    A news wire that prints file and line, and case cards with a severity-coloured spine.
    • Newswire
  5. theaaa.xyz
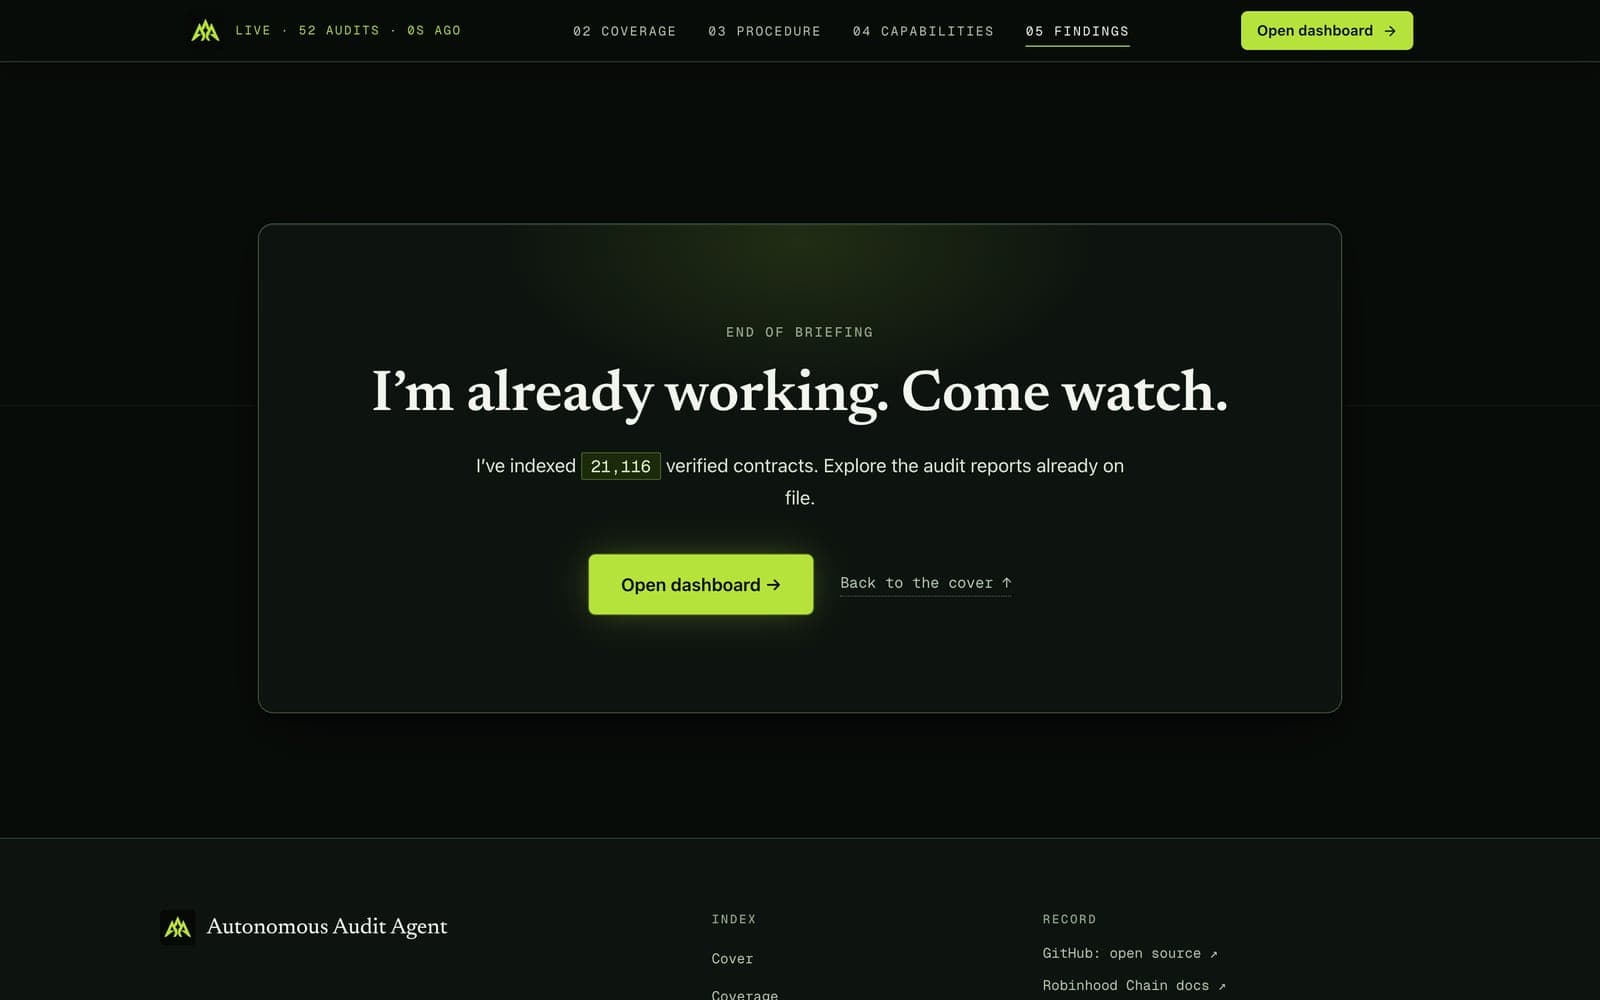
    The end of the briefing: “I’m already working. Come watch.”

    05 / 05 — End of briefing

    The close, again in the first person: “I’m already working. Come watch.”

    • First person
  1. theaaa.xyz/#stats
    Coverage on theaaa.xyz: 437 findings by severity, tiles for contracts, audits and networks, and the note that a label does not prove an exploit

    01 / 05 — Coverage

    Findings by severity, with the site’s own note that a severity label alone does not prove an exploit.

    • Live
  2. theaaa.xyz/#how
    The procedure: a sticky step index and the index illustration

    02 / 05 — Procedure

    A sticky step index with three illustrations: the index, the lookup and the eight-phase audit.

    • Scroll-spy
  3. theaaa.xyz/#features
    “Built for real audit work, not demos.”: the agent’s capability bento

    03 / 05 — Capabilities

    “Built for real audit work, not demos.”: an evidence bento and a severity taxonomy.

    • Bento
  4. theaaa.xyz/#findings
    Findings: a wire with file and line, and case cards with a severity-coloured spine

    04 / 05 — Findings

    A news wire that prints file and line, and case cards with a severity-coloured spine.

    • Newswire
  5. theaaa.xyz
    The end of the briefing: “I’m already working. Come watch.”

    05 / 05 — End of briefing

    The close, again in the first person: “I’m already working. Come watch.”

    • First person

CH. 02 / 06 — How it works

From an address to a case file

Scanners collect verified source from 15 EVM networks. An operator starts an audit from the contract page; the system extracts the code into a Foundry project, runs the multi-agent audit and writes the report back into the index.

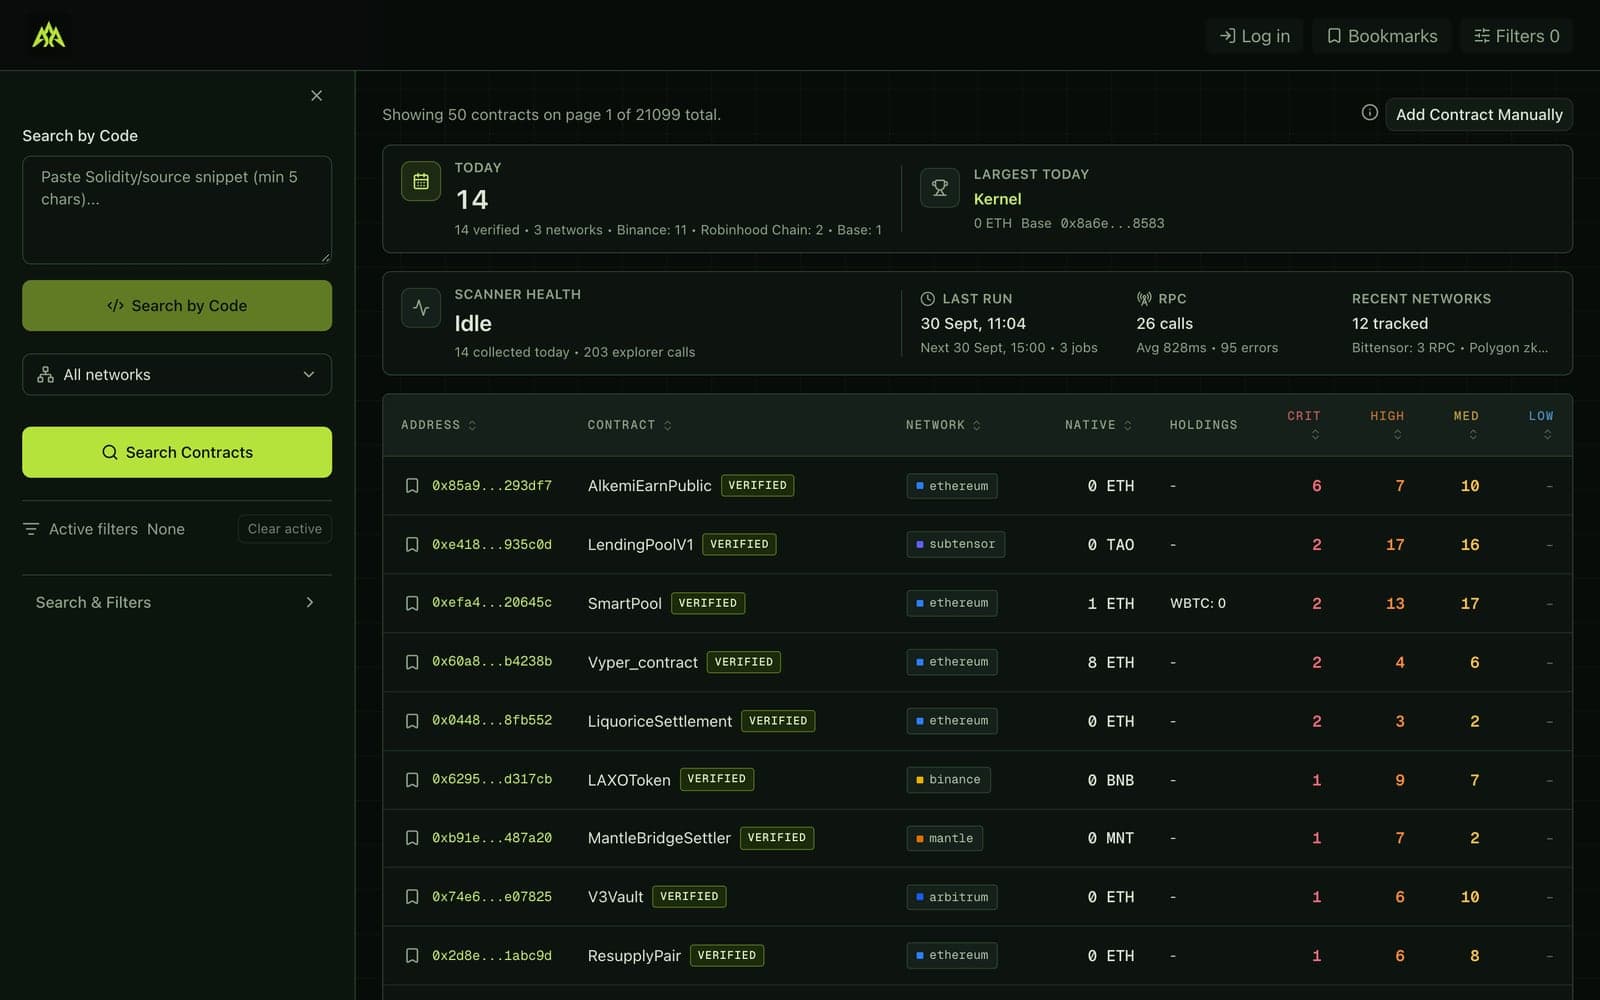
Scheduled scanners over public RPC: source, metadata, balances and proxy targets in one place, searchable by a line of code.
  • 15 networks
  • Public RPC only
  • Search by code

PL. 01 — The index

  1. 01

    The index

    Scheduled scanners over public RPC: source, metadata, balances and proxy targets in one place, searchable by a line of code.

    • 15 networks
    • Public RPC only
    • Search by code
    theaaa.xyz/dashboard
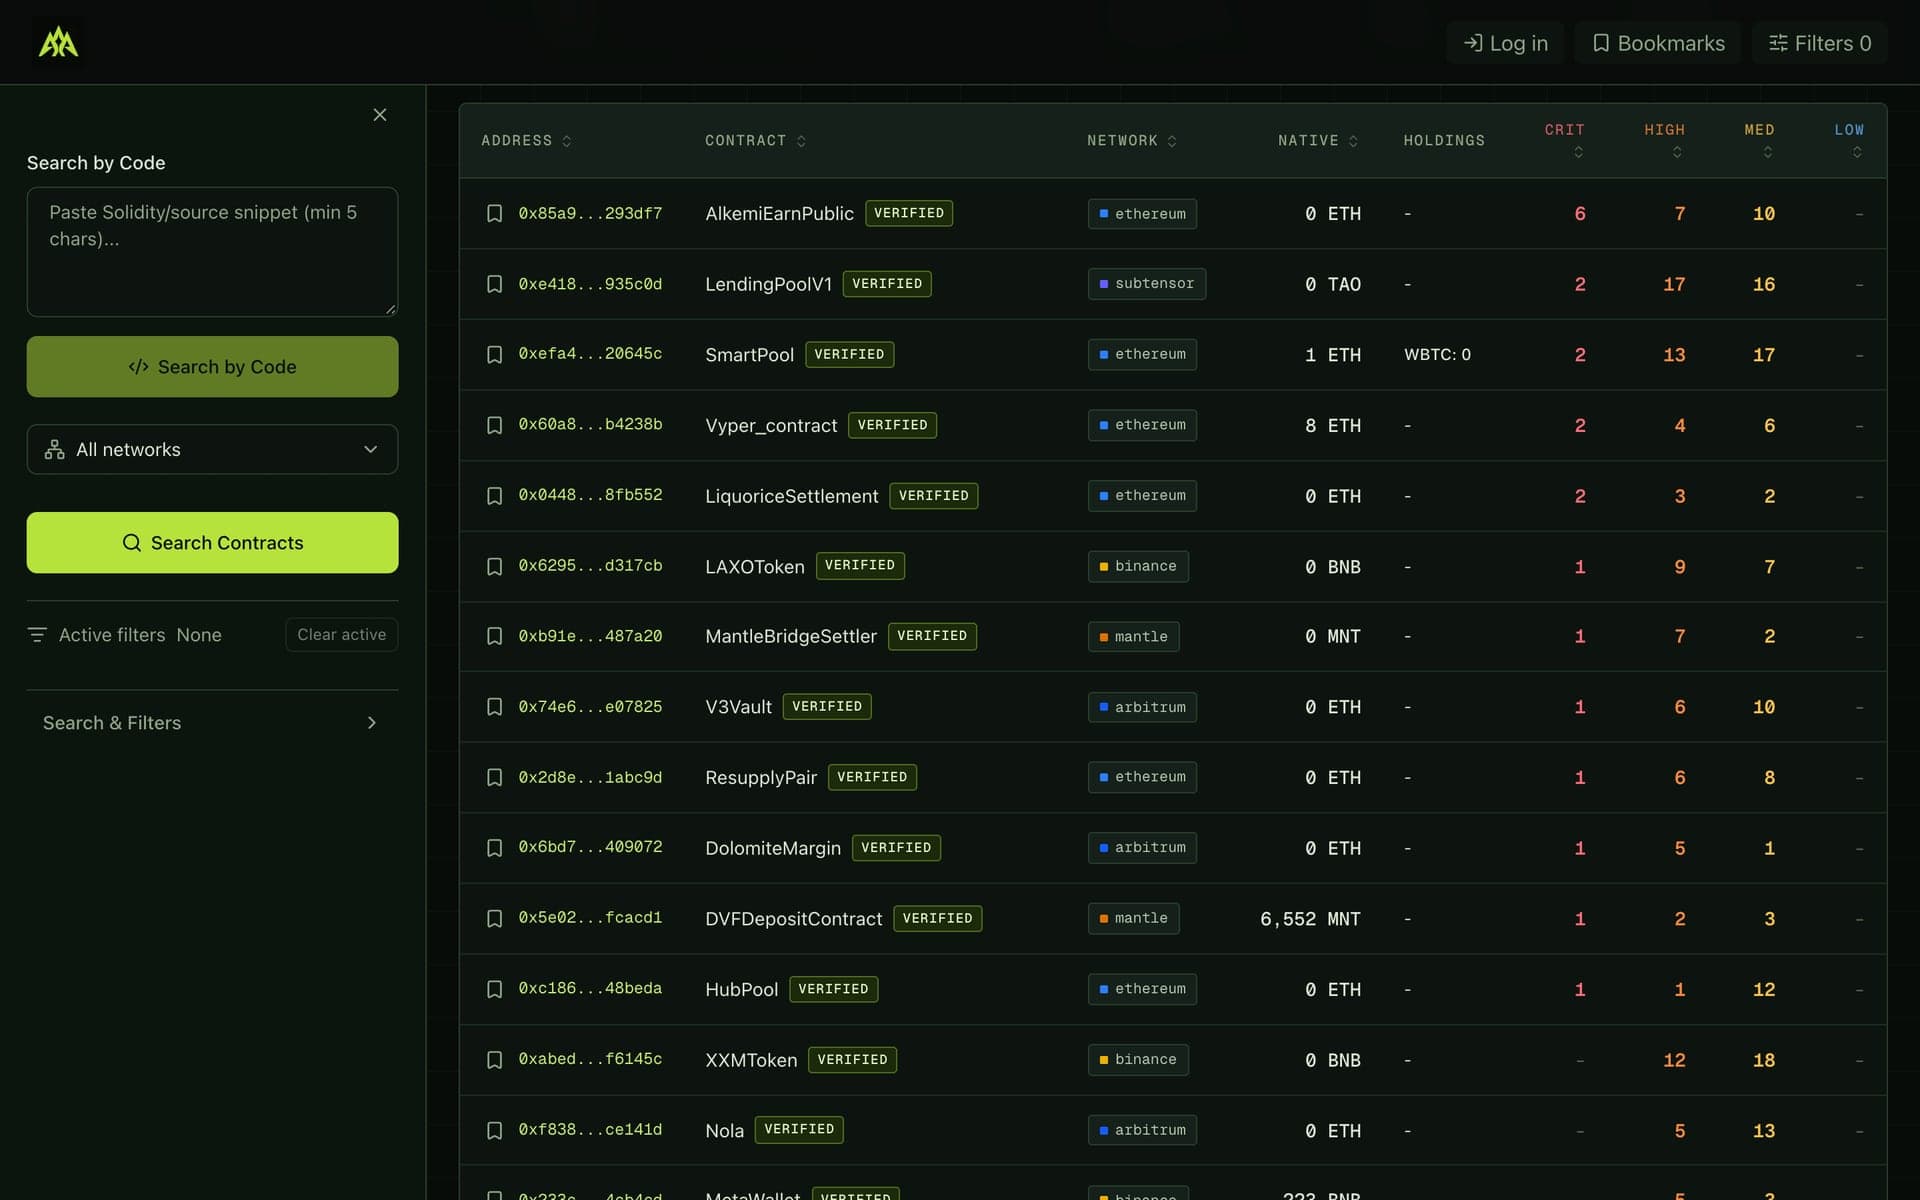
    The dashboard: search by code, scanner-health tiles and a table sorted by severity
  2. 02

    The verified source

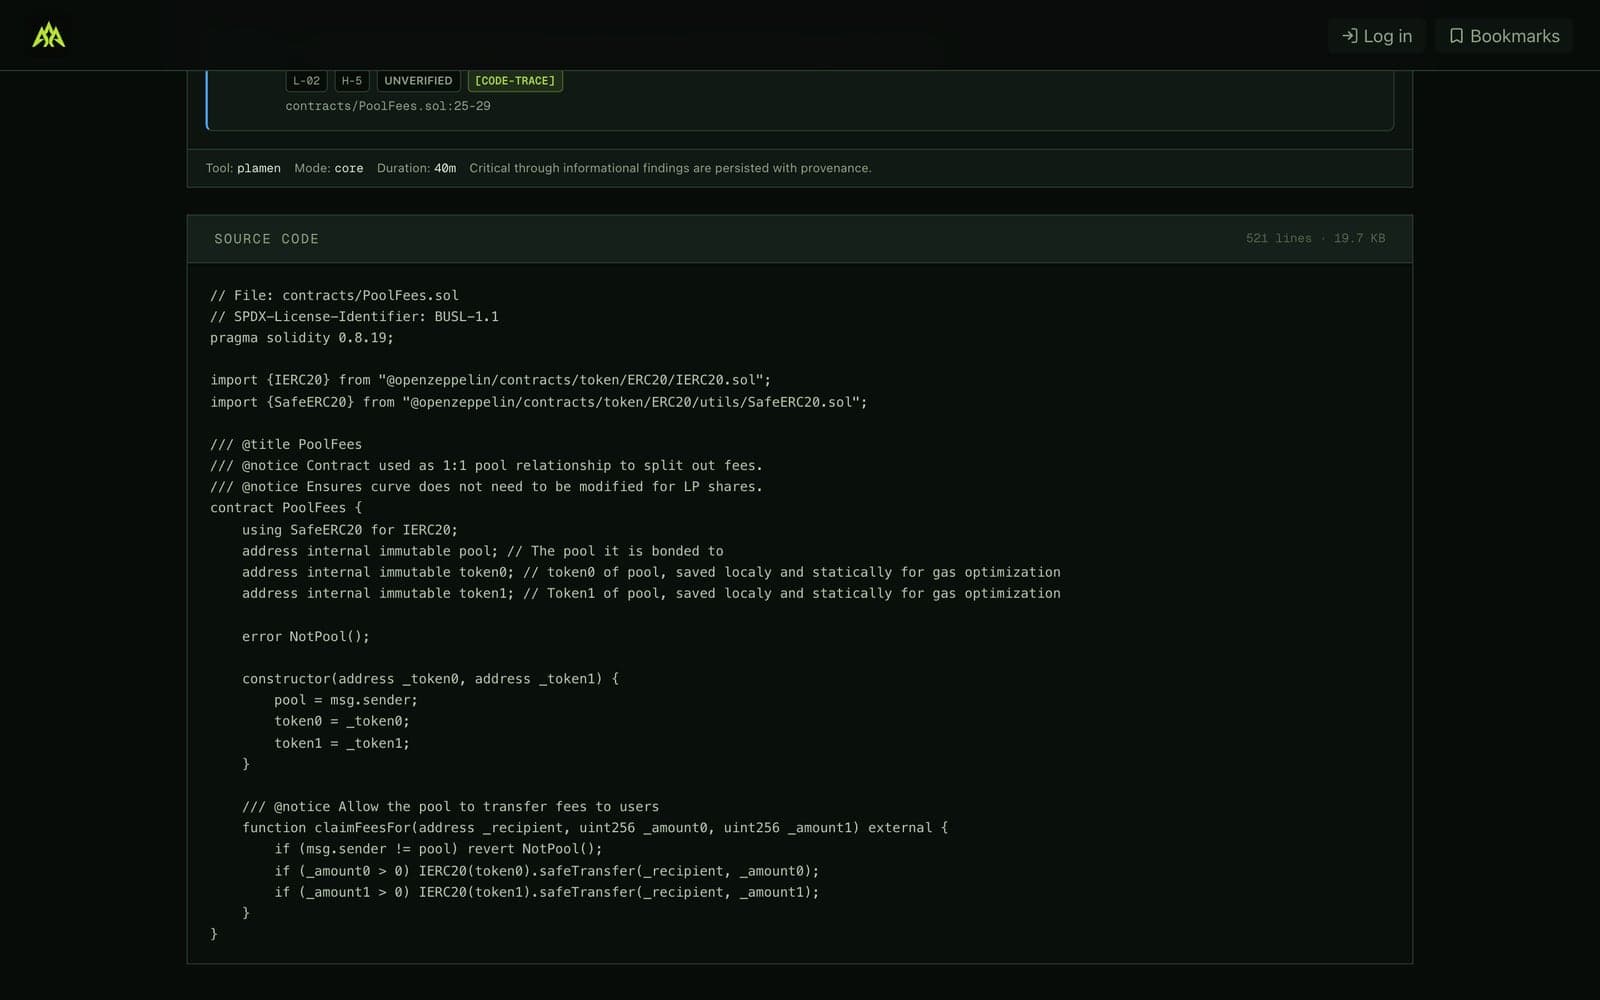
    Verified source is stored and readable on the contract page. For an audit it is extracted into a Foundry project with the exact compiler version.
    • Foundry
    • solc from metadata
    theaaa.xyz
    A contract’s verified source in the source viewer
  3. 03

    The audit

    Eight phases of multi-agent analysis. If the AI provider’s quota runs out, the audit pauses and resumes by itself, and the operator can cancel it from the dashboard.

    • 8 phases
    • Auto-resume

    Audit · Plamen

    Schematic · no real data

    Demo · schematic
    Framework
    Plamen · open source
    Phases
    8
    Workspace
    Foundry project
    Quota runs out
    pauses, then resumes by itself
    Cancel
    operator only
  4. 04

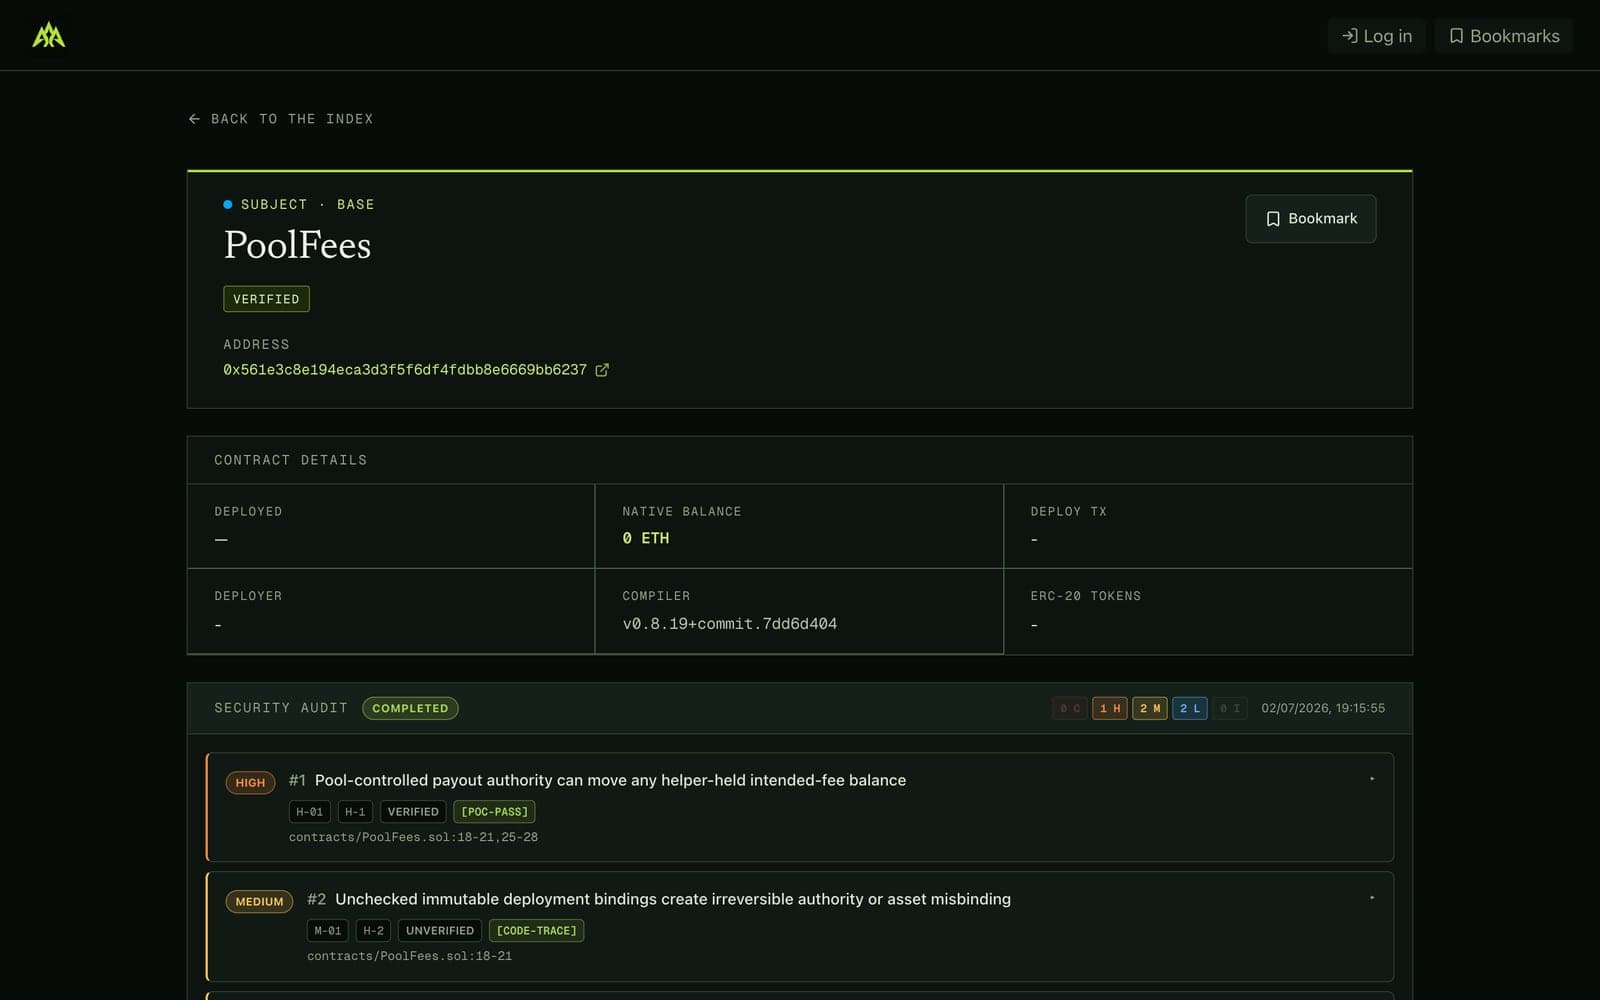
    The case file

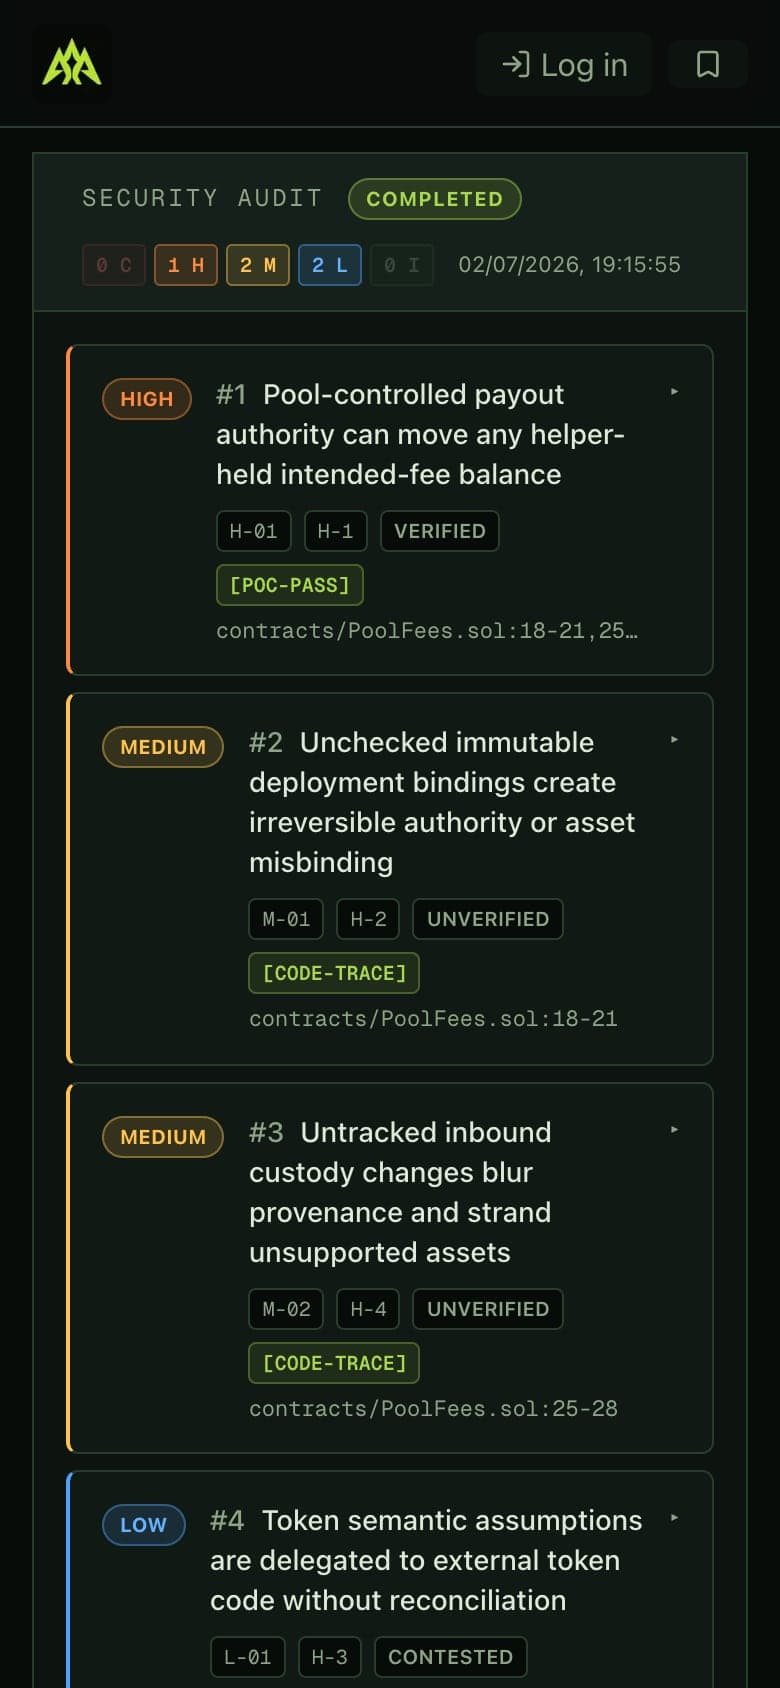
    The report is stored with every finding’s severity and location; the newest reports add a status and an evidence tag. Anyone can read it without signing up.
    • Severity + location
    • No signup
    theaaa.xyz
    A contract case file: the subject header, contract details and the start of the security audit
  1. 01

    The index

    Scheduled scanners over public RPC: source, metadata, balances and proxy targets in one place, searchable by a line of code.

    • 15 networks
    • Public RPC only
    • Search by code
    theaaa.xyz/dashboard
    The dashboard: search by code, scanner-health tiles and a table sorted by severity
  2. 02

    The verified source

    Verified source is stored and readable on the contract page. For an audit it is extracted into a Foundry project with the exact compiler version.

    • Foundry
    • solc from metadata
    theaaa.xyz
    A contract’s verified source in the source viewer
  3. 03

    The audit

    Eight phases of multi-agent analysis. If the AI provider’s quota runs out, the audit pauses and resumes by itself, and the operator can cancel it from the dashboard.

    • 8 phases
    • Auto-resume

    Audit · Plamen

    Schematic · no real data

    Demo · schematic
    Framework
    Plamen · open source
    Phases
    8
    Workspace
    Foundry project
    Quota runs out
    pauses, then resumes by itself
    Cancel
    operator only
  4. 04

    The case file

    The report is stored with every finding’s severity and location; the newest reports add a status and an evidence tag. Anyone can read it without signing up.

    • Severity + location
    • No signup
    theaaa.xyz
    A contract case file: the subject header, contract details and the start of the security audit

CH. 03 / 06 — Multi-agent audit

Many agents, one verdict

The audit runs on the open-source Plamen framework, in eight phases: recon, breadth, depth, fuzzing, attack chains, PoC tests, a skeptic and a judge, then the report. Dozens of AI agents share the work.

Demo · schematic

Recon

A map of the contract: functions, roles, external calls and known public incidents.

What it checks

  • Attack surface
  • Roles
  • Known incidents

Recon

Schematic · no real data

Demo · schematic
Functions
mapped
Roles & permissions
listed
External calls
traced
Public incidents
notes in the workspace
Illustrative schematic. Orders, names, amounts and messages are examples.
  1. 01 / 05 — RECON

    Recon

    A map of the contract: functions, roles, external calls and known public incidents.

    What it checks

    • Attack surface
    • Roles
    • Known incidents

    Recon

    Schematic · no real data

    Demo · schematic
    Functions
    mapped
    Roles & permissions
    listed
    External calls
    traced
    Public incidents
    notes in the workspace
  2. 02 / 05 — BREADTH

    Breadth

    Parallel agents sweep the whole codebase, each by its own vulnerability class.

    What it checks

    • Access control
    • Accounting
    • Oracles

    Breadth

    Schematic · no real data

    Demo · schematic
    Agents
    in parallel
    Scope
    the whole codebase
    Output
    hypotheses for depth
  3. 03 / 05 — DEPTH · FUZZ

    Depth & fuzzing

    Domain agents trace token flow and state while fuzz campaigns hunt for broken invariants.

    What it checks

    • Token flow
    • State
    • Invariants

    Depth & fuzzing

    Schematic · no real data

    Demo · schematic
    Token flow
    traced
    State transitions
    traced
    Invariants
    fuzz campaign
  4. 04 / 05 — CHAIN · POC

    Chains & PoC

    Weak findings are combined into chains, and serious hypotheses get a Foundry test that has to pass.

    What it checks

    • Attack chains
    • Foundry tests
    • POC-PASS · POC-FAIL

    Chains & PoC

    Schematic · no real data

    Demo · schematic
    Chains
    precondition → postcondition
    Foundry test
    has to pass
    No executed test
    tagged CODE-TRACE
  5. 05 / 05 — JUDGE · REPORT

    Judge & report

    A skeptic challenges serious findings, a judge decides, and demoted findings stay visible in the report with their original severity.

    What it checks

    • Skeptic & judge
    • Visible demotions

    Judge & report

    Schematic · no real data

    Demo · schematic
    Skeptic
    challenges
    Judge
    decides
    Demotion
    visible, with the original severity
Illustrative schematic. Orders, names, amounts and messages are examples.

CH. 04 / 06 — Honest severity

Every finding says how it was checked

In the newest reports every finding carries a status and a tag: a passing PoC test, a code trace only, or contested and demoted. The demotion stays visible and the original severity is kept.

Route

PL. 01 — The whole audit: PoolFees on Base, five findings

Route
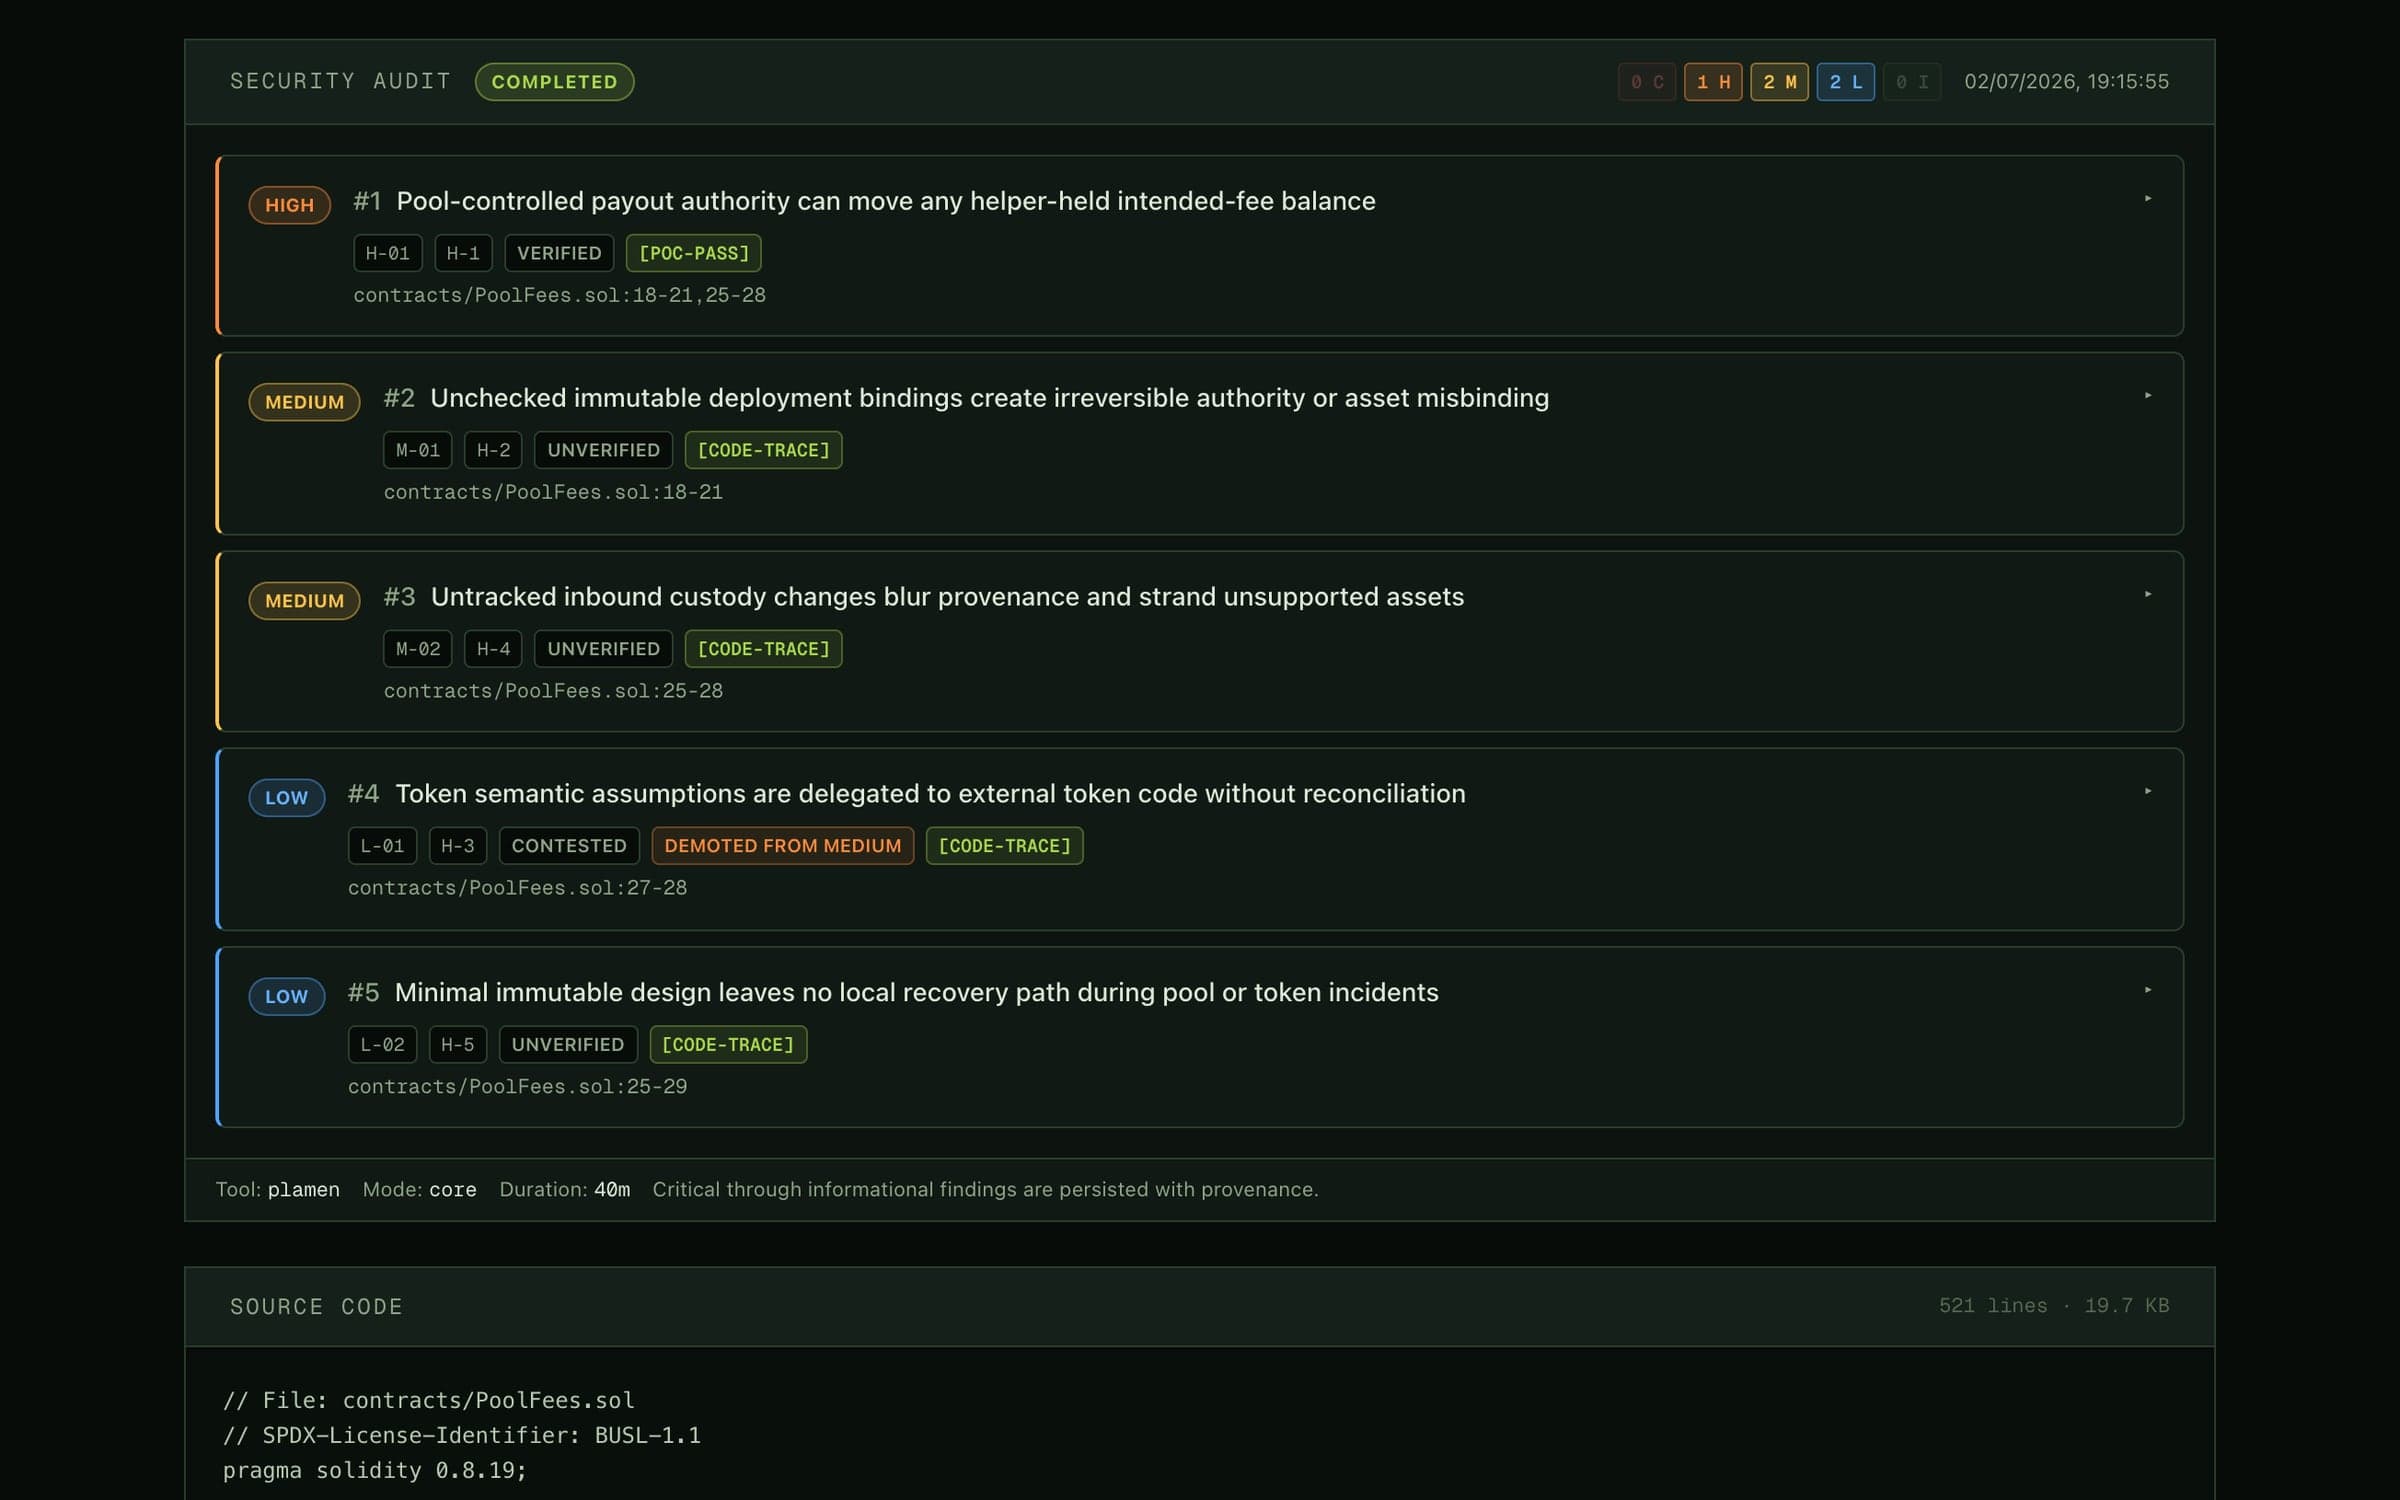
  1. 01The whole audit: PoolFees on Base, five findings
  2. 02Verified · the PoC test passed
  3. 03Unverified · a code trace only
  4. 04Contested · demoted from Medium
  5. 05Tool, mode and duration
Open the full image (opens in a new tab)
The PoolFees audit on Base: five findings with status and tag — VERIFIED with POC-PASS, UNVERIFIED with CODE-TRACE, CONTESTED and demoted from Medium

Route

  1. 01The whole audit: PoolFees on Base, five findings
  2. 02Verified · the PoC test passed
  3. 03Unverified · a code trace only
  4. 04Contested · demoted from Medium
  5. 05Tool, mode and duration
Open the full image (opens in a new tab)

CH. 05 / 06 — Autonomy with rules

Autonomous, not unsupervised

AAA reads and indexes by itself. An audit starts when the operator launches it, and anything that leaves the system, such as a message to a protocol or a public post, waits for the owner’s review and approval.

Demo · schematic
  • Rule: review first, send second

AAA

Autonomous Audit Agent

Block explorersreads only
Public RPCreads only
CoinGeckoreads only
Public incidentsreads only
Foundry audit runswrites after a “yes”
Audit reportswrites after a “yes”
Protocol messagessends after confirmation
Public postssends after confirmation

01 / 03 — reads only

Illustrative schematic. Orders, names, amounts and messages are examples.

AAA

Autonomous Audit Agent

Block explorersreads only
Public RPCreads only
CoinGeckoreads only
Public incidentsreads only
Foundry audit runswrites after a “yes”
Audit reportswrites after a “yes”
Protocol messagessends after confirmation
Public postssends after confirmation

Reads by itself

Verified source from block explorers, public RPC, prices and public incident notes, stored in its own PostgreSQL index.

  • Block explorersreads only
  • Public RPCreads only
  • CoinGeckoreads only
  • Public incidentsreads only

Audits after the operator’s “yes”

An audit starts only when the operator launches it from the contract page; its report is written to the index.

  • Foundry audit runswrites after a “yes”
  • Audit reportswrites after a “yes”

Sends only with approval

Messages to protocols and public posts go through the owner’s review first.

  • Protocol messagessends after confirmation
  • Public postssends after confirmation
  • Rule: review first, send second
Illustrative schematic. Orders, names, amounts and messages are examples.

AAA

Autonomous Audit Agent

Reads by itself

Verified source from block explorers, public RPC, prices and public incident notes, stored in its own PostgreSQL index.

  • Block explorersreads only
  • Public RPCreads only
  • CoinGeckoreads only
  • Public incidentsreads only

Audits after the operator’s “yes”

An audit starts only when the operator launches it from the contract page; its report is written to the index.

  • Foundry audit runswrites after a “yes”
  • Audit reportswrites after a “yes”

Sends only with approval

Messages to protocols and public posts go through the owner’s review first.

  • Protocol messagessends after confirmation
  • Public postssends after confirmation
  • Rule: review first, send second
Illustrative schematic. Orders, names, amounts and messages are examples.

CH. 06 / 06 — Result

21,000 contracts, 52 audits

The index grows with every scan, and every report is open to anyone without signing up. The counts were read from theaaa.xyz on 30 Sep 2026.

  1. Fork and first deploy
  2. First multi-agent audit
  3. AAA and theaaa.xyz
  4. The Dossier design
  5. A new green identity
  • 21K+

    contracts indexed

  • 15

    EVM networks

  • 52

    completed multi-agent audits

  • 437

    recorded findings

  • 8

    audit phases

A case file’s findings list on a phone, with the evidence tags
  • Severity labels come from the reports themselves and are not, on their own, proof of an exploit.
  • Built on the open-source BugChainIndexer project; audits run on the open-source Plamen framework. The latest audit on file is from 2 July 2026.

Plates

PL. 01—04

theaaa.xyz
AAA: the homepage “I hunt smart-contract bugs. On my own.” with its live counter manifest — Scroll preview
PL. 01 — AAA · Scroll previewOpen the full-page image (opens in a new tab)
The contract dashboard: CRIT, HIGH, MED and LOW columns for every contract
PL. 02 — AAA · desktop
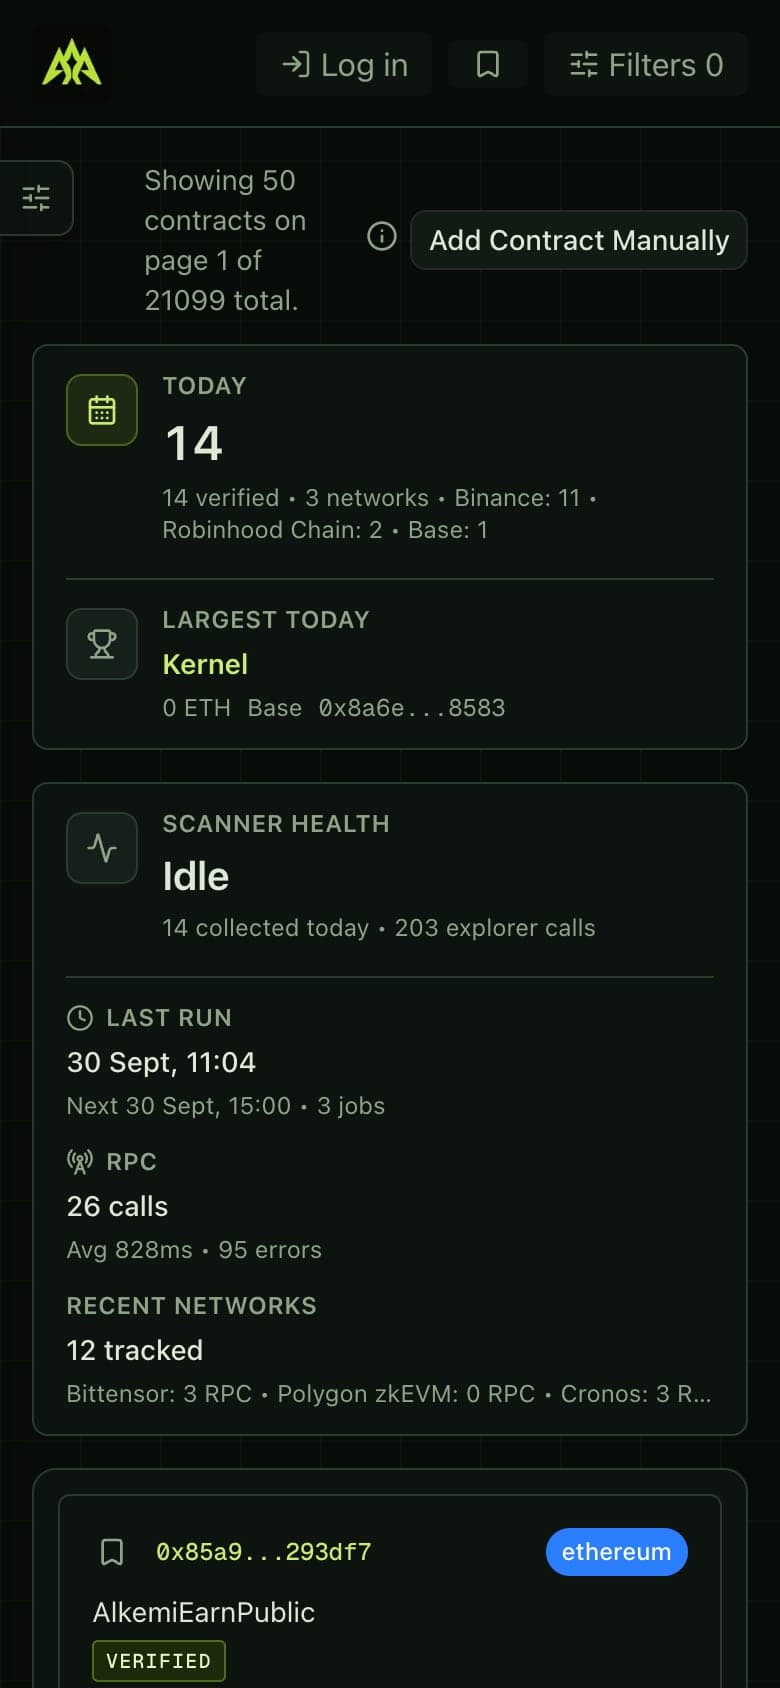
The dashboard on a phone: the TODAY and SCANNER HEALTH tiles
PL. 03 — AAA · mobile
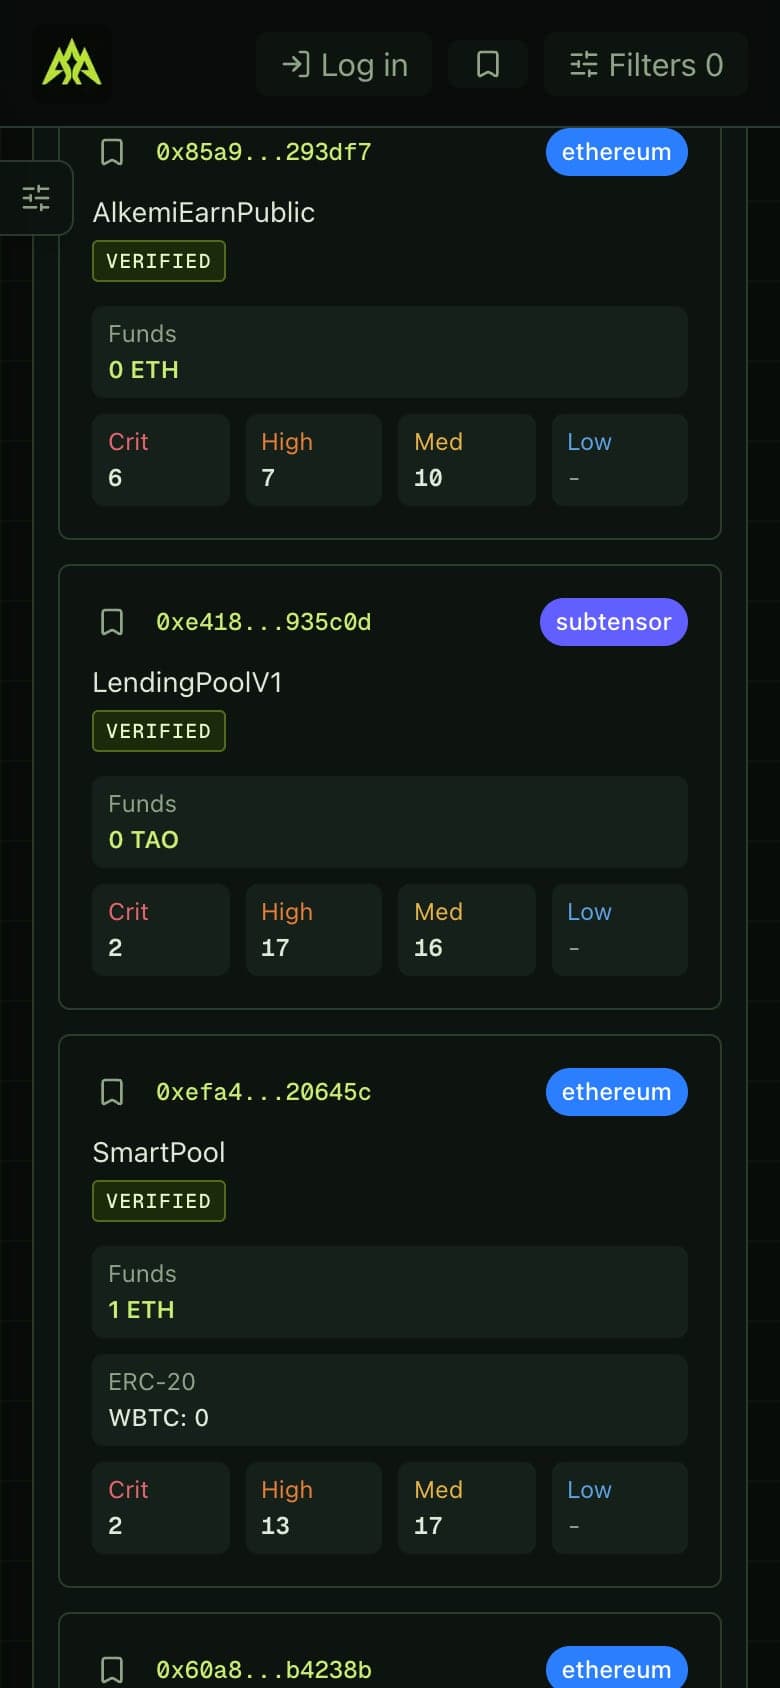
Contract cards on a phone, with finding counts by severity
PL. 04 — AAA · mobile

Palette & type

  • #080C09Graphite
  • #1B2B20Moss
  • #B6E33BField green
  • #D9F596Pale lime
  • #F2F6EEPaper
  • Newsreader
  • Geist
  • Geist Mono

Contact

Want something like this?

Your project could be Fig. 07.

30 minutes, no commitment. You’ll leave with concrete ideas for your website, processes or product.

FIG. 07 — Your project30 minutes · no commitment · we reply within a few hours on business days